 CAIN-42 CAIN Studio
CAIN-42 · Verified Record · 2026-11-13
A verification result, not a certification.
A CAIN-42 Verified Record says one narrow, testable thing: this specific bundle passed its own standalone verifier, and the file digests match. It does not say the vendor is certified, the tests are good, or the action was safe.
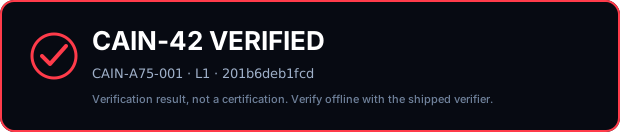
Example: verified-cain-a75-001.json · the signed bundle
What it proves
| Proves | Does not prove |
|---|---|
| The bundle's own verifier accepted the signed record. | That the record is complete or that the underlying action was safe. |
| The signature matches the pinned issuer key. | That the issuer is independent or that the quorum is a witness network. |
| The file digests match the bytes present. | That a test is good or that a certification exists. |
| The Proof Standard level checked (L1–L4). | That the customer's control environment is effective. |
How to verify it yourself
python3 -m cain_verify.cli <bundle> --json
# or inside the bundle:
python3 verify_offline.py
The verifier imports no CAIN code. Pin the key out of band; never trust the bundle's own public_key.txt until it matches your pin.
Use of the mark
The mark may be displayed only next to the exact bundle it names, with a link to the JSON and the offline verifier. Do not use it to imply that CAIN-42 certifies an organization, a product, or a control environment. The mark is licensed under the offer ladder; the verifier itself stays open and free.
Proof Standard · Pricing and Proof SLA · Integrations · Agentic 75 · Contact: firmeai2026@gmail.com